
Training · ICS / OT Security
ICS Defence 101
Learn to defend industrial control systems on a real cyber-physical range, from logging and SIEM detection to protecting live PLCs.
- Beginner+
- 40 hours
- 5 days
- 5-day bootcamp
About the course
ICS Defence 101 takes you from core IT security principles to the realities of defending industrial control systems, and explains why OT and IoT environments need a different approach from enterprise IT.
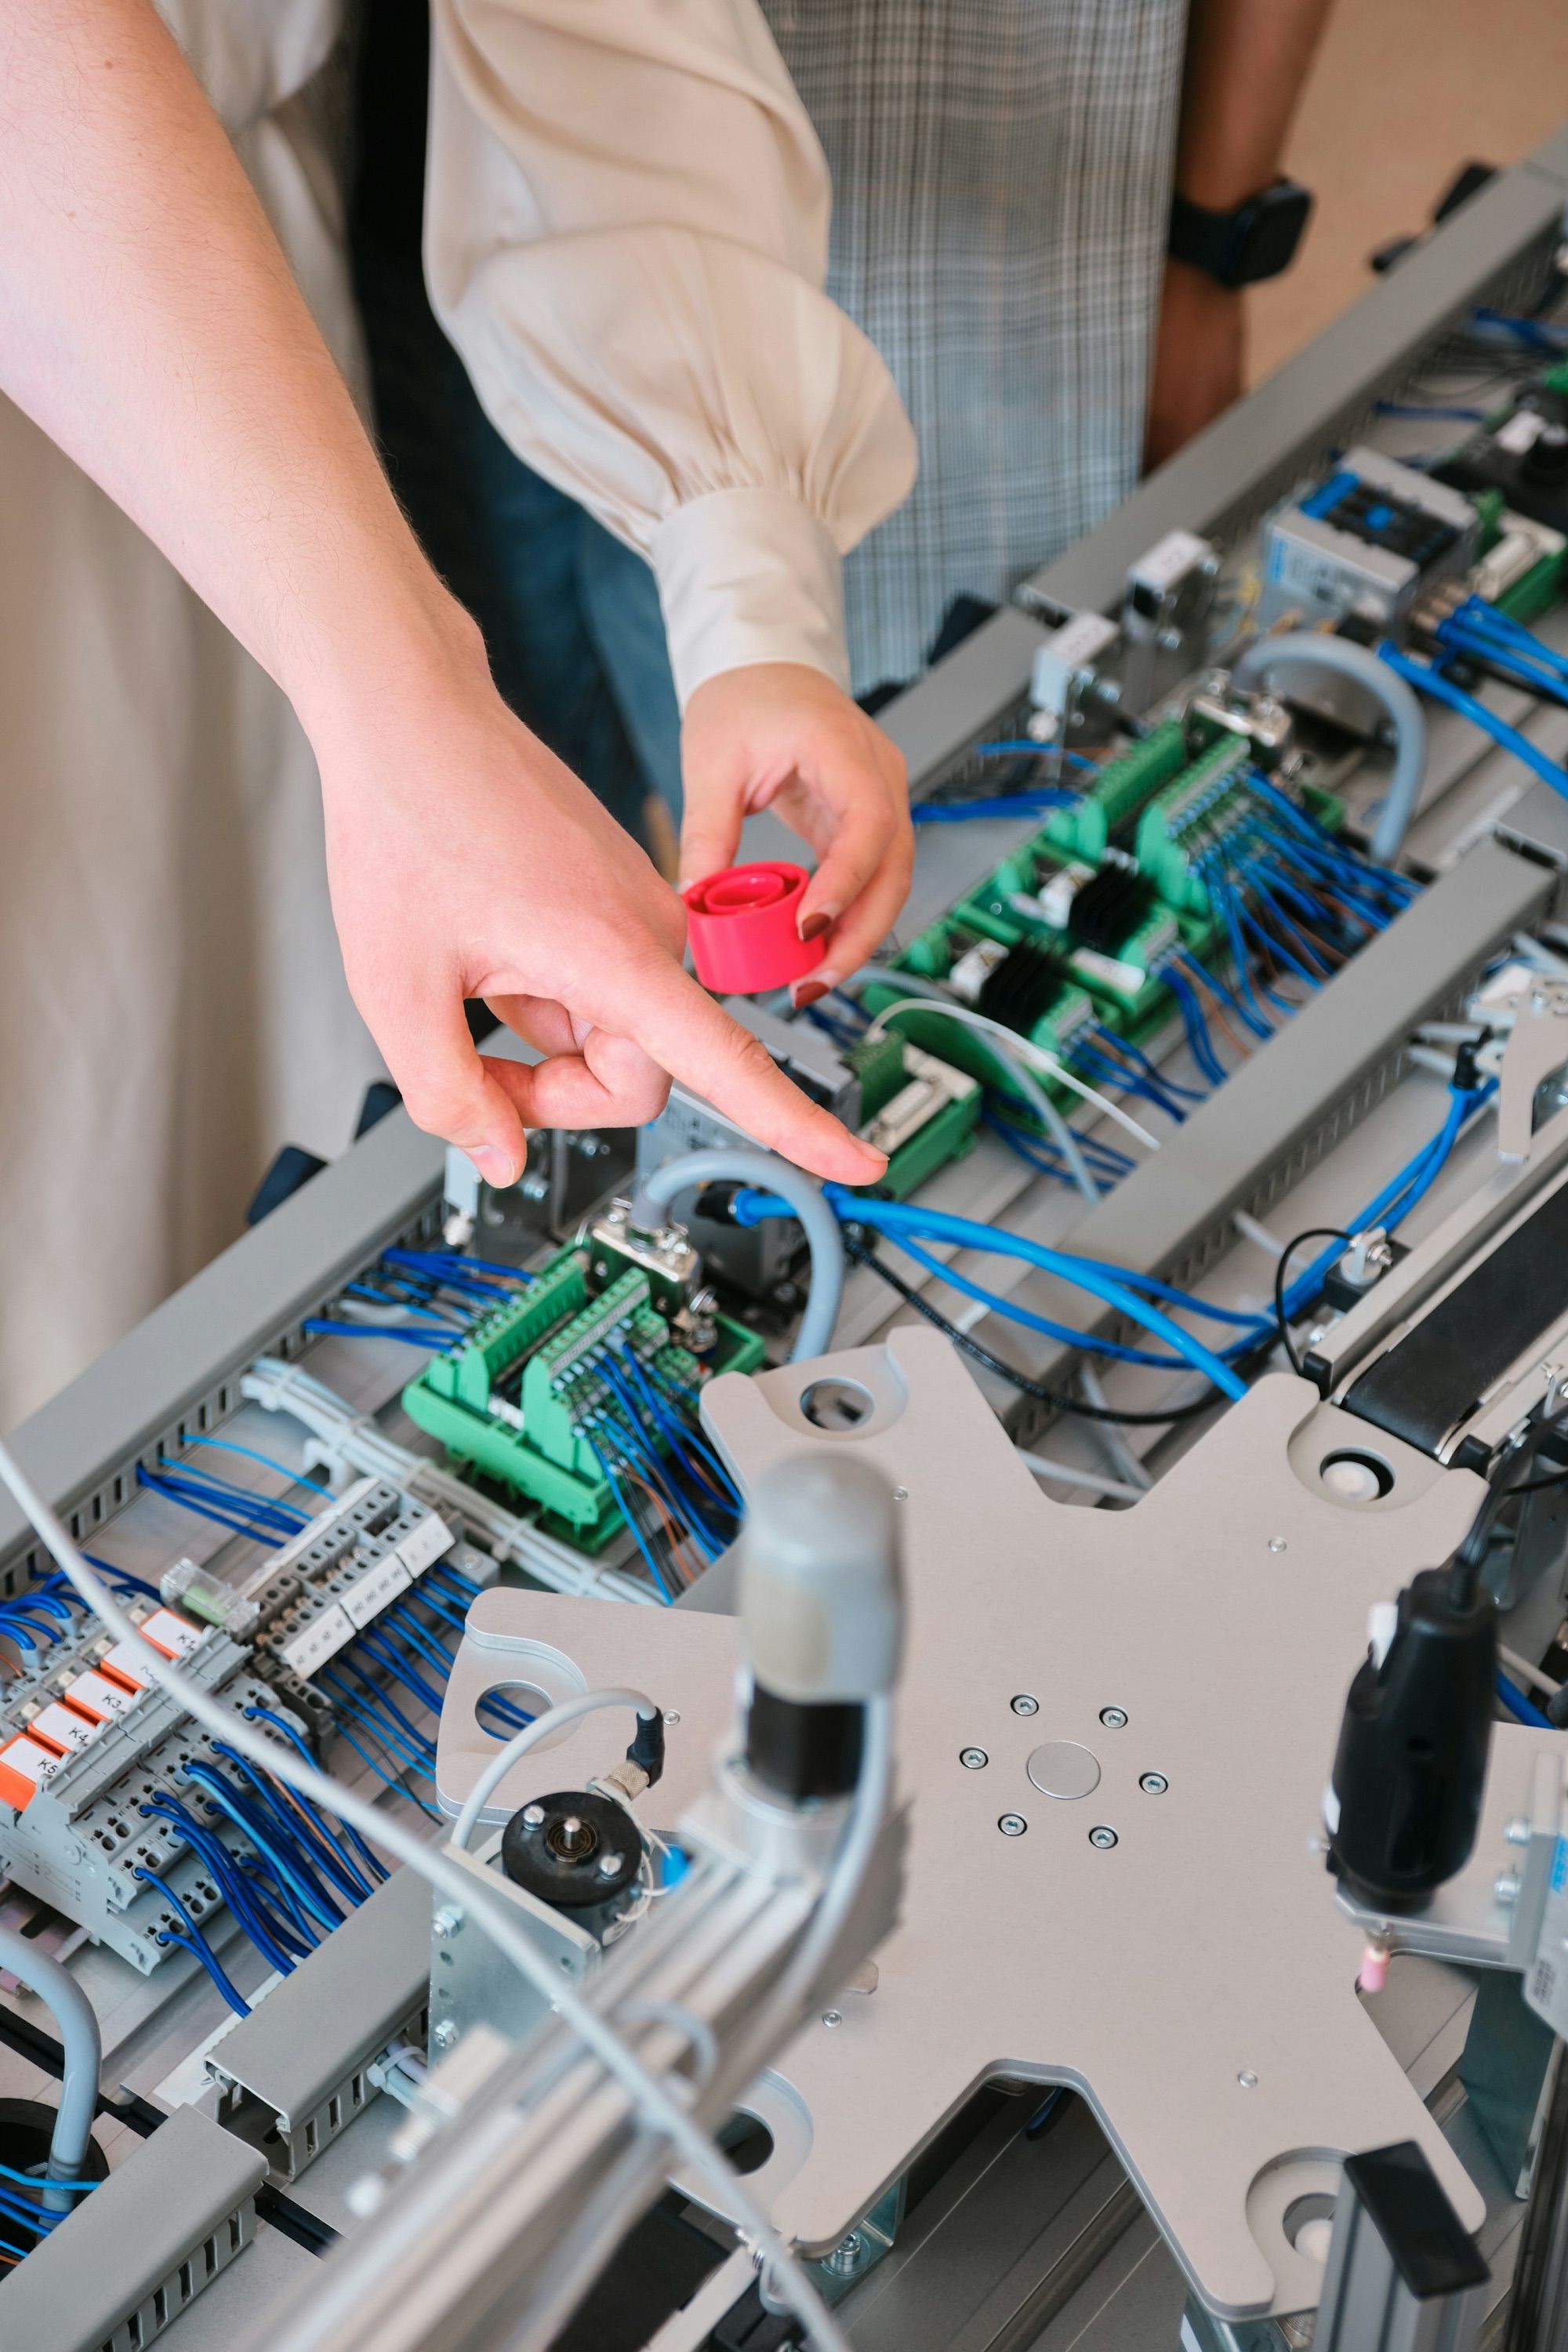
Every session pairs theory with lab work on a simulated industrial environment built from real PLCs, field nodes and sensors. You build, attack, monitor and defend the same environment over the week.
Who should attend
- SOC analysts and IT security engineers moving into OT
- Control-system, automation and plant engineers
- IT and OT network and infrastructure administrators
- Incident responders supporting industrial sites
- Cyber security students and recent graduates
What the course covers
Six topics in focus
01
IT, IoT and OT infrastructure
How enterprise, IoT and control networks connect, and where they differ.
02
ICS security challenges
Legacy assets, proprietary protocols and availability-first operations.
03
Monitoring and logging
Collecting and retaining logs from OS, network and OT devices.
04
SOC management and alerts
SIEM use cases, alert tuning and SOC workflows for IT and OT.
05
Preventive measures
Hardening, segmentation, ICS-aware IDS and secure remote access.
06
Regulations and audits
IEC 62443, NERC CIP and log-retention compliance.
Tools and technologies
- Siemens PLCs
- Wireshark
- Suricata
- Snort
- Modbus
- DNP3
- OPC UA
- IEC 61850
Course outline
5 days, one capstone
- Day 1 Foundations PLCs, HMIs, SCADA, the Purdue model, and building the lab.
- Day 2 Visibility OS, network and OT logging, a local SIEM and IT incident response.
- Day 3 Know the attack surface ICS protocols, safe scanning, PLC attacks and risk assessment.
- Day 4 Defend the plant Hardening, segmentation, OT monitoring, secure remote access and OT response.
- Day 5 Put it together Advanced labs across the full IT-to-OT stack, and the capstone.
Capstone
Attack and defence
Teams defend the range against a live, scored attack scenario.
Outcomes
You will be able to
- Collect IT, network and OT logs into a working SIEM
- Build use cases and alerts tuned for industrial protocols
- Safely map an ICS network and assess its exposure
- Harden and segment OT using the Purdue model
- Run an OT-aware incident response with minimal disruption
Before you join
Prerequisites
- No prior OT or ICS experience needed
- Basic networking (TCP/IP, ports and protocols)
- Comfortable with the Windows and Linux command line
Learning path
Take before
Cyber Security 102
Turn the basics into hands-on skills. Scan networks, test web apps and harden systems in a safe lab, then switch sides to detect and respond.
Beginner+ · 30 hours · 5 weeks · Live online
View course
Take next
Advanced ICS Security
Defend the modern industrial edge across private wireless, cloud-connected OT, identity-first access and the software supply chain.
Advanced · 40 hours · 5 days · 5-day bootcamp
View courseGet the full syllabus
Batches start every month from January 2027. Send us an enquiry and we'll email you the detailed brochure and the next batch dates.